user@l1ghtn1ng:~$ ls -la blog/
5 entries - 8 tags
grep --tag
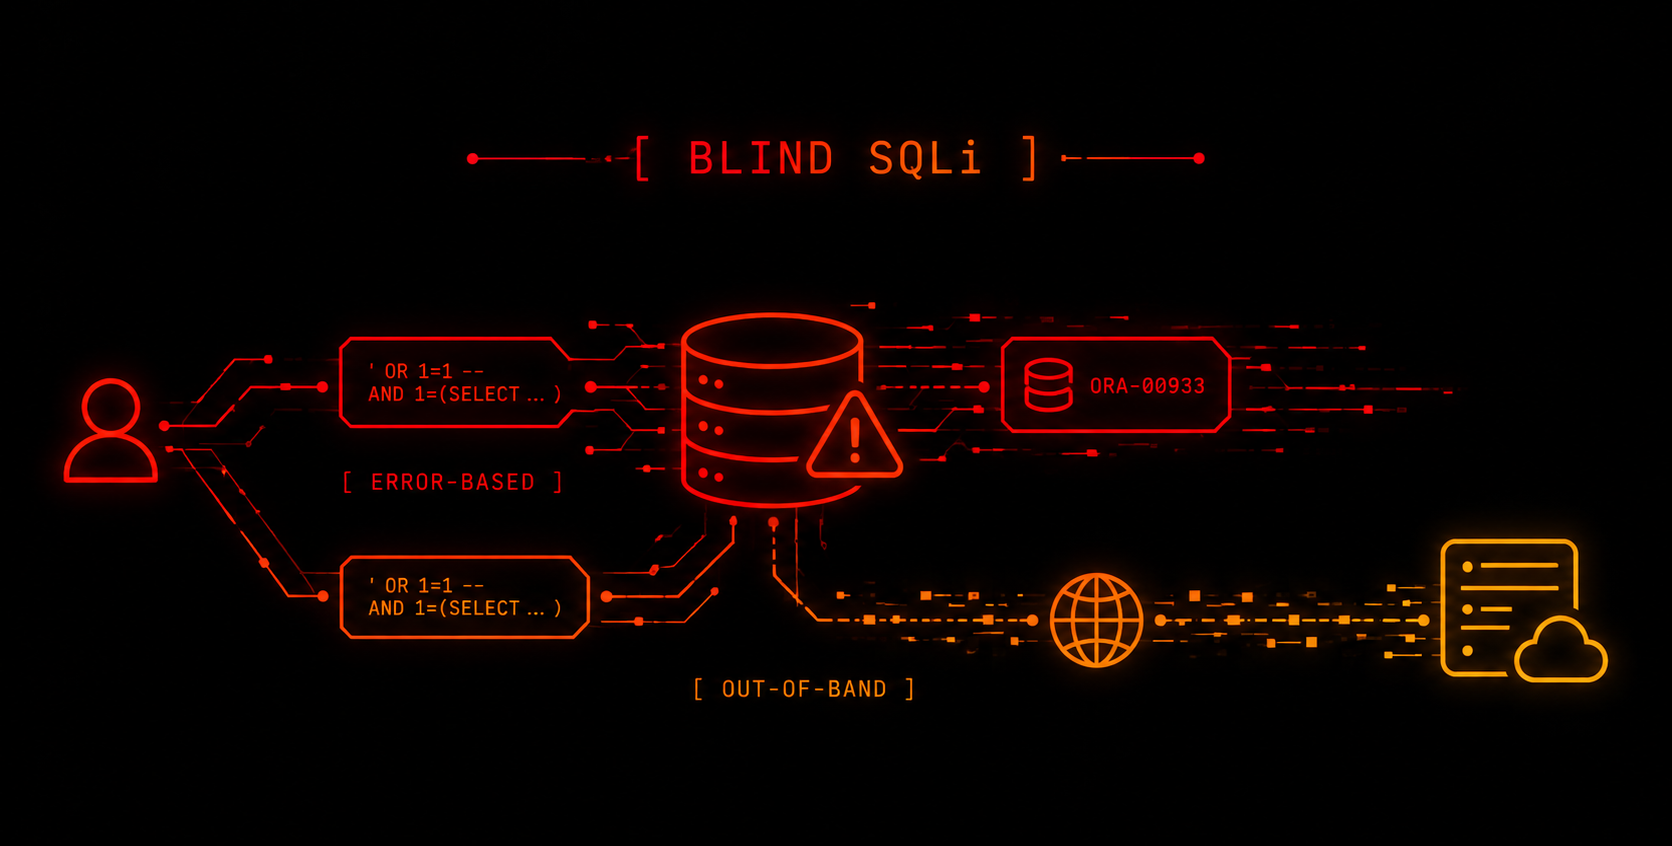
Blind SQLi: Conditional Errors, OOB, and WAF Evasion
I walk through different Blind SQLi scenarios in a practical way, from conditional errors in Oracle to OOB exfiltration through SQLi and XXE, also covering a WAF bypass using XML encoded payloads.
- #WebSecurity
- #BurpSuite
- #hacking
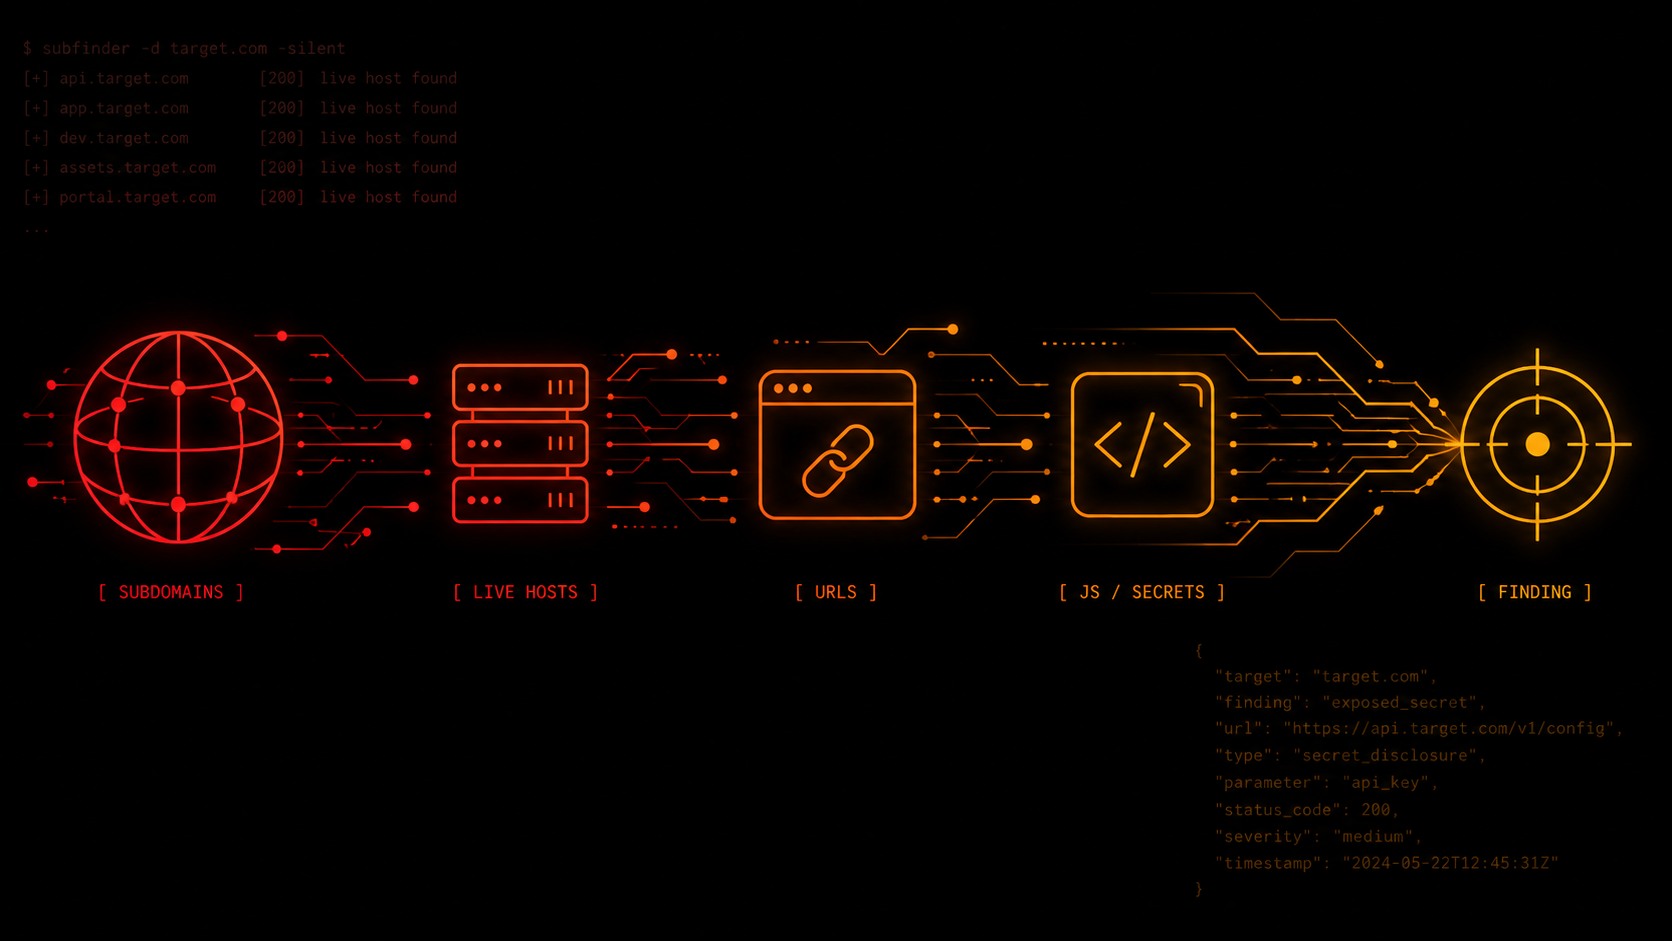
My Recon Methodology (and How I Ended Up Automating It Into a Single Tool)
Recon is one of the most important parts of bug bounty, and also the most repetitive. This is the order and the tools that work for me, phase by phase, and the tool I built so I wouldn't have to do it all by hand again.
- #BugBounty
- #Recon
- #Tooling
How I intercepted and impersonated a government chatbot by controlling a single parameter
Here's how an unvalidated URL parameter on a government chatbot turned into a full MITM over its WebSocket: I intercepted messages, impersonated the bot, and stole other people's chat history without a session.
- #BugBounty
- #write-up
- #ChatBot
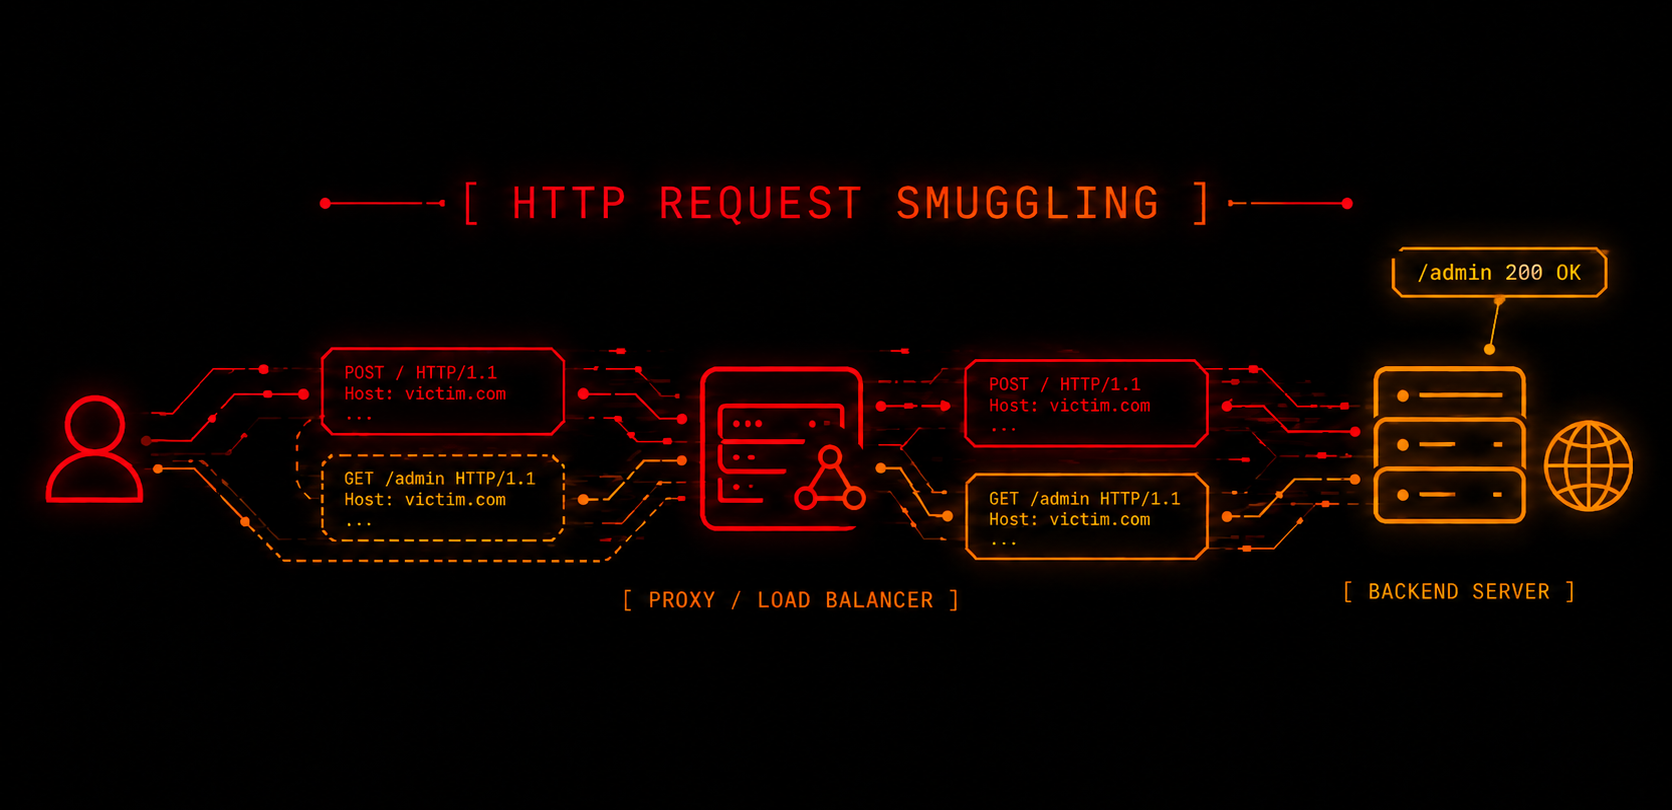
Learning HTTP Request Smuggling step by step
I explain how HTTP Request Smuggling works, how to detect it, and how to exploit it with practical examples.
- #WebSecurity
- #hacking
- #BurpSuite
How I got NASA's LoR by exploiting an Authentication Bypass
In this post I'll tell you how I found a vulnerability in NASA, and how you can start looking for one too ⚡
- #BugBounty
- #write-up
- #hacking